An employee opens an attachment, installs a program or visits a website that later turns out to be untrustworthy. Often, nothing noticeable happens. But when malicious software runs or an attacker gains access to a device, a single workstation can become the starting point for a wider security incident.
Modern endpoint protection must therefore do more than block known viruses. Organisations also need to recognise when a device behaves unusually, investigate what has happened and intervene quickly if necessary. Technologies such as EDR and XDR play an important role in this.
The workstation is an entry point into the organisation
An endpoint is a device that has access to the IT environment. This includes desktops, laptops and servers, but, depending on the solution used, may also include other devices. Employees use these systems to work with business applications, open documents and access data and network resources.
The risks also extend beyond the office. Employees work from home, while travelling or at customers' premises. Laptops connect to different networks and are sometimes used outside the direct oversight of IT management.
This makes it necessary to apply protection on the device itself. A well-secured business network provides insufficient protection when a laptop becomes infected outside the office and subsequently reconnects to the business environment.
Why traditional antivirus is not enough
Traditional antivirus software focuses primarily on identifying and blocking known malicious files and patterns. This remains valuable, but attacks do not always use recognisable malware.
An attacker may, for example, misuse existing system tools, execute unusual commands or attempt to collect login credentials. Individual actions may appear legitimate, while the combination points to an attack.
Modern endpoint protection therefore examines not only files, but also behaviour and events on the device.
Antivirus and preventive endpoint protection
Focuses on preventing known or suspicious software from causing damage. The protection checks files, processes and activities and can block harmful actions.
Key question: can we prevent this threat from being executed?
EDR: detection and investigation on endpoints
EDR stands for Endpoint Detection and Response. The solution records relevant events and analyses behaviour to identify potential attacks. During an incident, this information helps establish what has happened and what appropriate measures to take.
Key question: what is happening on this device, and do we need to intervene?
Prevention and EDR are not mutually exclusive alternatives. They complement each other. Prevention aims to stop an attack; EDR helps identify and investigate activities when preventive measures prove insufficient.
What can EDR reveal?
An EDR solution collects security-relevant information about activities on endpoints. This may include processes being started, programs making changes, suspicious commands and connections to other systems.
Assessing events together can reveal behaviour that may not be immediately apparent when checks are carried out in isolation.
Suspicious processes
— Unusual programs or commands that may indicate misuse of a device.Unusual behaviour
— Activities consistent with attempts to bypass security, elevate privileges or retain access.Suspicious connections
— Communication with external systems or other devices that warrants further investigation.Investigation and response
— Information to assess what prompted an alert and its potential consequences, and to isolate a device where necessary.
Not every deviation is an attack. Management software, updates and legitimate work can also cause unusual behaviour. Assessment therefore remains necessary: an alert is a reason to investigate, not automatic proof of a security incident.
In practice: suspicious activity on a workstation
An employee notices nothing, but the protection detects unusual behaviour
An employee opens a document received by email. Shortly afterwards, an unusual process starts on the laptop and attempts to execute additional commands and connect to an external system.
The employee can continue working as usual and notices no disruption. However, the endpoint protection detects the combination of activities and generates an alert. Assessment shows that the actions are inconsistent with normal use of the device.
The laptop is temporarily isolated from the business network, allowing further investigation without unnecessary risk to other systems. Investigators then establish which processes have run, whether any data has been accessed and what recovery measures are needed.
The difference lies not only in identifying suspicious software, but above all in the ability to make the course of a potential attack visible and take targeted follow-up action.
This is an illustrative example, not a description of a specific customer incident.
What does XDR add?
EDR focuses primarily on events on endpoints. But an attack is rarely confined to a single device. An attacker may also use stolen accounts, email, cloud applications or network connections.
XDR stands for Extended Detection and Response. Its underlying principle is to bring together security signals from different sources and analyse them in context. Depending on the solution, this may involve data from endpoints, identities, email, cloud environments and networks.
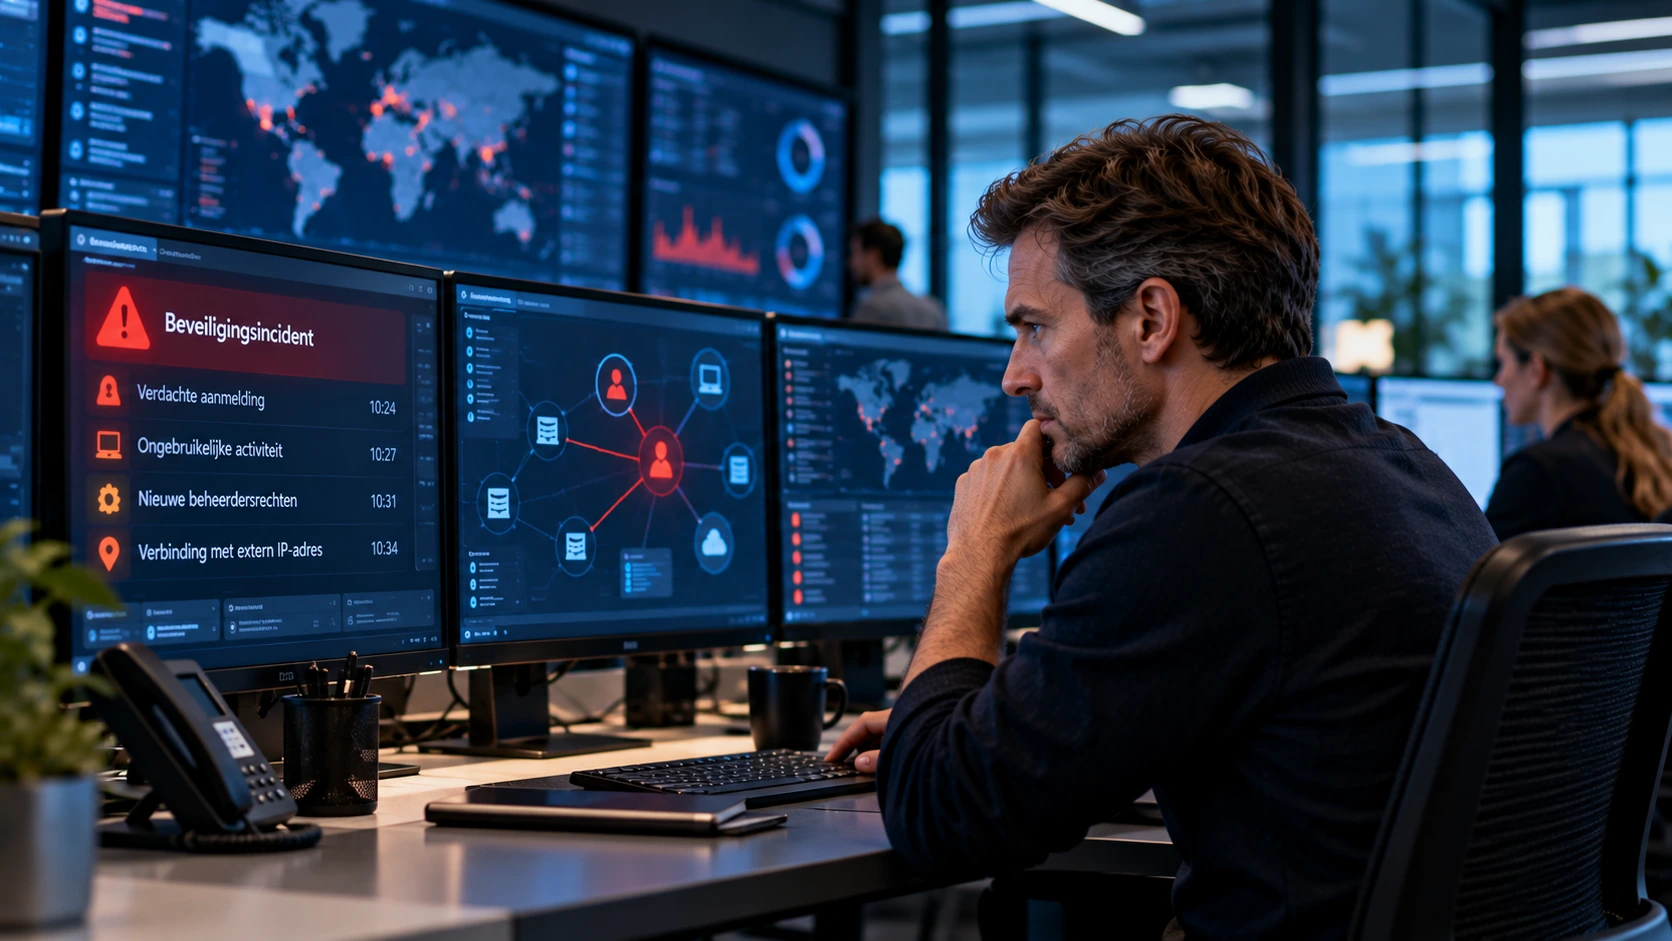
Suppose an account signs in from an unusual location, a suspicious process starts on a laptop shortly afterwards, and an attempt is then made to connect to an unknown external system. Separate security products may record these events individually. Combining the signals makes the potential connection apparent sooner.
XDR can therefore help improve incident detection and investigation. However, capabilities vary between suppliers and depend on the sources actually connected. Using the term XDR does not, therefore, guarantee that every part of the IT environment is automatically monitored.
An alert only has value when someone acts
A common misconception is that installing EDR software is enough to protect the organisation adequately. In reality, detection is only one part of security.
A solution can flag suspicious activities, but someone must then assess whether an incident has actually occurred, which systems may be involved and whether immediate intervention is necessary.
The way alerts are handled must therefore be clear in advance.
Detect
— The security solution identifies suspicious activities and records relevant events.Assess
— A specialist investigates the alert, determines its severity and establishes whether further action is needed.Intervene
— Where necessary, processes are stopped, devices are isolated or other measures are taken to limit further damage.Recover and improve
— The cause and consequences are investigated, normal operation is restored and findings are used to improve security.
Security incidents can also occur outside office hours. Organisations must therefore agree when alerts will be assessed, who is authorised to intervene and how serious incidents will be escalated.
A security product that generates alerts without clear follow-up offers less protection than the presence of that technology might suggest.
Not every device is automatically protected
Endpoint protection only works on devices where the necessary protection is actually installed and active. This may seem obvious, but in practice systems can fall out of view.
Consider a laptop that has not been used for a long time, a new server on which security software has not yet been installed, or a device that no longer communicates correctly with the central management platform.
Professional endpoint management therefore also includes checking coverage: which devices are present, which are protected and where are security measures missing?
Mobile phones, tablets and personal devices sometimes have different technical capabilities. They require additional measures, such as device management, access conditions and protection of business data. Not every device can be protected with EDR in the same way.
Endpoint protection is part of a wider whole
EDR and XDR are important elements of modern security, but they do not replace other measures. Good patch management reduces the presence of known vulnerabilities. Identity and access management prevents unnecessarily broad permissions. Network segmentation can limit the consequences if a device is compromised despite the protection in place.
Backup and recovery also remain necessary. If an attacker causes damage despite all the measures taken, the organisation must be able to rely on dependable recovery arrangements.
The strength of endpoint protection therefore lies in its integration with the rest of IT management. Security signals need to be understood in the context of users, devices, applications and network connections.
From installed software to demonstrable protection
The most important question is not whether a security product is installed on every workstation. It is whether the organisation knows which devices are protected, whether suspicious activities are recognised in time and whether effective follow-up is in place.
This requires a combination of technology, expert assessment and clear responsibilities.
Good endpoint protection does not prevent every incident. It does, however, increase the likelihood that an attack will be recognised early, its consequences will remain limited and the organisation can take targeted action when needed.