An employee takes on a new role, an external specialist is brought in temporarily or a colleague leaves the organisation. In all these situations, the access rights needed to carry out the work change. Yet those changes are not always processed consistently. An employee retains access to applications from a previous role, a temporary account remains active or no one knows exactly which permissions an external party has been given.
Identity and access management therefore involves more than creating user accounts and setting passwords. It concerns who may access which systems and data, the basis on which that access is granted and how the organisation checks whether the permissions remain appropriate. This matters for security, but also for keeping the IT environment clear and manageable.
Access rights change as the organisation changes
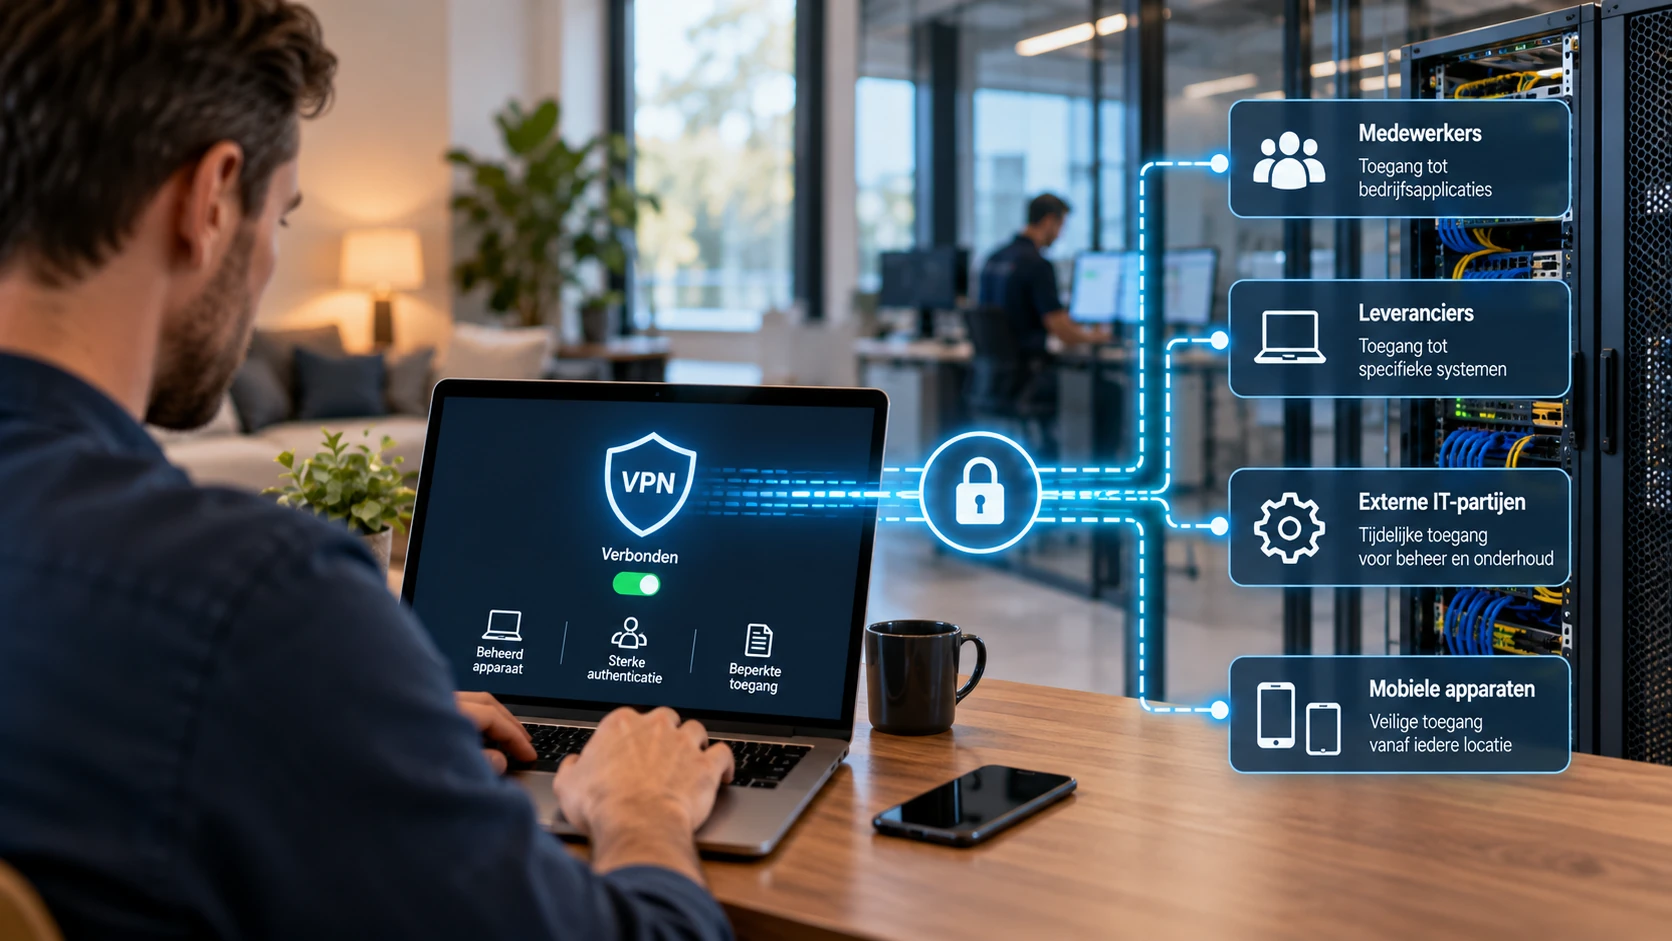
In a small organisation, it is often still reasonably clear who uses which applications. As a business grows, this becomes more complicated. Employees change roles, departments introduce new systems and suppliers become involved in specific tasks. At the same time, new forms of access emerge through cloud applications, mobile devices and remote connections.
Access rights are usually added when someone needs something. Removing permissions receives less attention in practice, particularly when an employee changes roles within the organisation. As a result, permissions can gradually accumulate. Someone who once worked in finance, for example, may still have access to financial data even though that access is no longer necessary for their current role.
This is also known as privilege creep: the unnoticed expansion or retention of access rights. The risk is not only that employees can do more than they need to, but also that misuse of an account can have more serious consequences.
What does good identity and access management involve?
Effective access management consists of several complementary measures. No single measure is sufficient on its own.
Reliable identification
— Every user has a recognisable personal identity, so it is clear who is being given access and activities are not unnecessarily carried out through shared accounts.Strong authentication
— Signing in is protected by appropriate measures, including multifactor authentication (MFA), so a password alone is not enough.Appropriate permissions
— Users are given access only to the applications, data and functions necessary for their work.Review and follow-up
— Access rights are adjusted when circumstances change, reviewed periodically and withdrawn when they are no longer needed.
These measures need to be implemented together. An account protected by MFA can still have too many permissions. And carefully assigned permissions provide insufficient protection if an account remains active after an employee leaves.
Authentication and authorisation are different things
Two terms are often confused in access management. Authentication is about establishing who someone is. Authorisation determines what that person is then allowed to do.
For example, an employee can sign in to Microsoft 365 using a personal account and MFA. This establishes their identity with a certain degree of confidence. Which SharePoint environments, Teams channels or business applications they can then access is determined by the permissions granted.
That distinction matters. Strong authentication reduces the risk of unauthorised people signing in with stolen credentials, but does not prevent a legitimate account from accessing data without a business need. Both signing in and the permissions available afterwards therefore need to be managed carefully.
The access rights lifecycle
Access management is not a one-off configuration exercise. Permissions need to evolve with users' work and responsibilities. Four stages are important here.
Request access
— The permissions required are determined on the basis of the role, tasks and systems someone needs to use.Grant access
— The request is approved in accordance with the agreed responsibilities and the permissions are configured appropriately.Adjust and review access
— When roles change, new tasks arise or periodic reviews take place, the organisation establishes whether existing permissions are still necessary.Terminate access
— When someone leaves or completes their work, accounts and permissions are withdrawn promptly, including any active sessions and additional means of access.
The third stage deserves particular attention. Clear procedures often exist for employees joining and leaving, but internal role changes are not always processed in the same way. This is precisely how unnecessary permissions can remain in place for years.
Good cooperation between HR, line managers, application owners and IT management is therefore essential. The line manager knows what work someone carries out, while IT management can handle the technical configuration. Without clear agreements on who requests, approves and reviews permissions, responsibility can easily become unclear.
A new role, but the old permissions remain
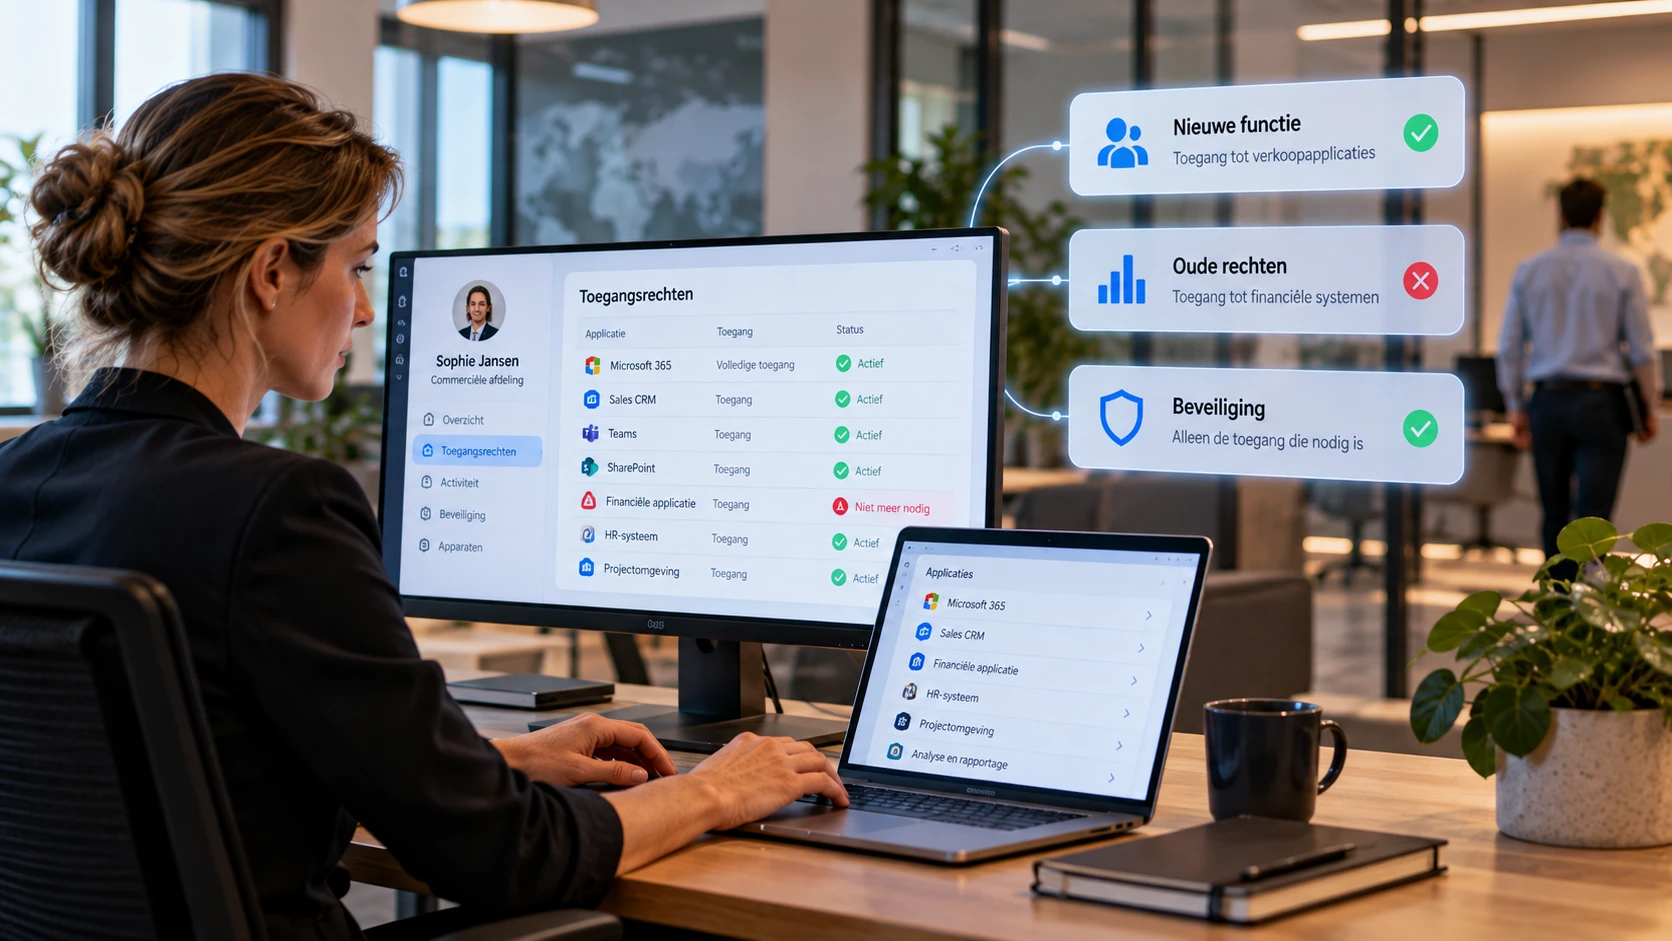
An employee in the finance department takes on a new role in the commercial department. IT management ensures that the employee gains access to the sales applications and shared documents they need. However, their existing access to financial systems remains unchanged because no one has requested that these permissions be withdrawn.
The employee can carry out their work without difficulty, and there is no visible fault or security alert. Yet the account now has more permissions than necessary. If the account is misused, financial data unrelated to the current role may consequently also be accessible.
The problem does not arise because the technology is not working properly, but because the role change was considered only in terms of new permissions. Good access management therefore requires not just granting access, but also reviewing and withdrawing existing permissions.
Administrator accounts need extra protection
Not every account has the same capabilities. A standard user can generally work only within their assigned applications and data. An administrator can change settings, create users, adjust security measures or gain access to large parts of the IT environment.
Accounts with elevated permissions therefore need extra protection. An important principle is that administrators should not unnecessarily carry out their everyday work using an account with extensive administrative privileges. Separating regular user activities from administrative tasks reduces the chance of an incident on a workstation immediately affecting the wider infrastructure.
It must also be clear which individuals and external parties have administrative privileges, what those privileges are used for and whether they are needed permanently. Where possible, elevated permissions can be granted temporarily and their use can be subject to additional monitoring.
For example, an external supplier carrying out maintenance on a business application may temporarily need elevated permissions. Agree in advance which permissions are needed and for how long, monitor their use and withdraw them once the work is complete.
Who decides which access is necessary?
IT management can establish the permissions an account has from a technical perspective, but cannot always independently assess whether they are necessary for the business. A system administrator knows, for example, which employees have access to a financial application, but the responsible manager or application owner must be able to determine whether that access is appropriate for their work.
Good access management therefore requires a clear allocation of responsibilities. The organisation decides which access is necessary and permitted. IT management ensures that those decisions are implemented correctly in technical terms and that deviations become visible.
This also applies to external parties. A supplier may need access to a specific application or server, but that need does not automatically justify permanent or broad access. The organisation must be able to determine which permissions are granted, how long they are needed and who is responsible for reviewing them.
Centralised configuration helps, but does not solve everything
Many organisations use Microsoft Entra ID or a comparable identity service to manage user accounts, authentication and application access centrally. This offers significant benefits. Users can sign in to multiple applications with a single identity, security requirements can be applied centrally and account management becomes clearer.
Yet a centralised identity configuration does not automatically mean that all access rights are managed centrally. Some business applications have their own user accounts or permissions. Permissions within applications, shared files and collaboration environments can also be assigned separately.
An organisation therefore needs to look beyond its central user directory and consider actual access within the applications it uses. Otherwise, an account may be correctly configured centrally while excessive or outdated permissions still exist within an application.
Access management needs ongoing attention
A well-designed access model can lose its value over time if changes are not processed consistently. New applications are added, employees take on different responsibilities and external parties are given access for temporary projects. Without periodic reviews, the gap grows between the permissions once granted and those actually needed.
Access management therefore belongs within routine IT management. This involves not only creating and removing accounts, but also reviewing permissions, identifying deviations and clearly documenting responsibilities. It requires both technical measures and agreements within the organisation.
The aim is not to impose as many restrictions as possible on employees. The aim is for everyone to have the access they need to do their work well, while preventing unnecessary permissions and unmanaged access.