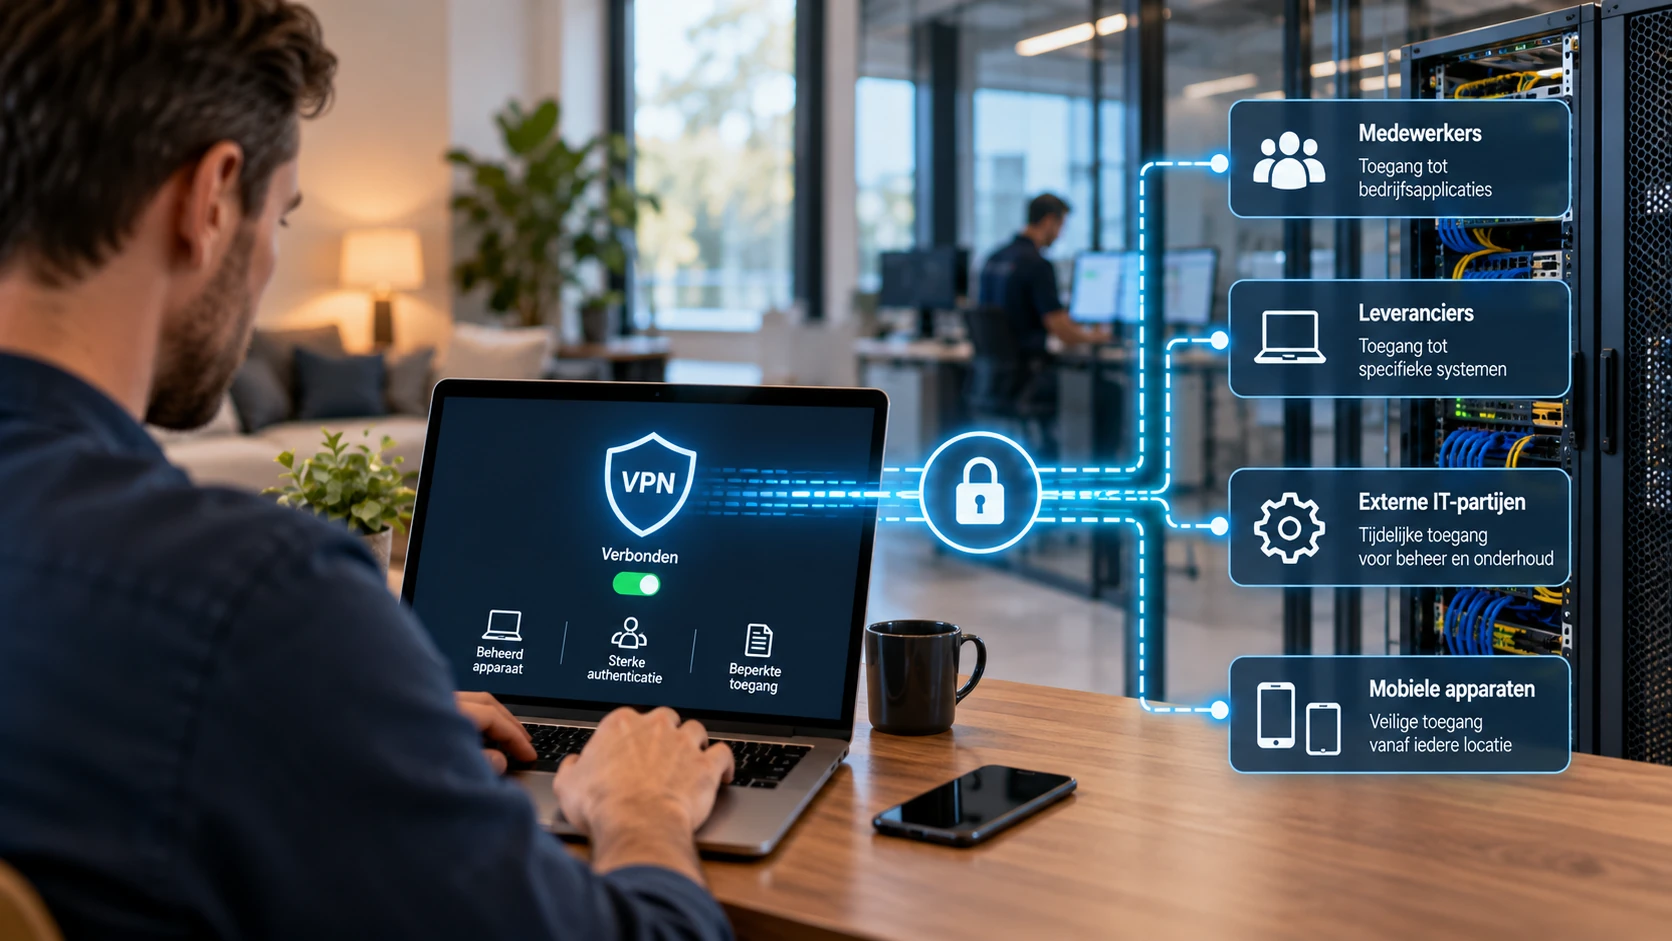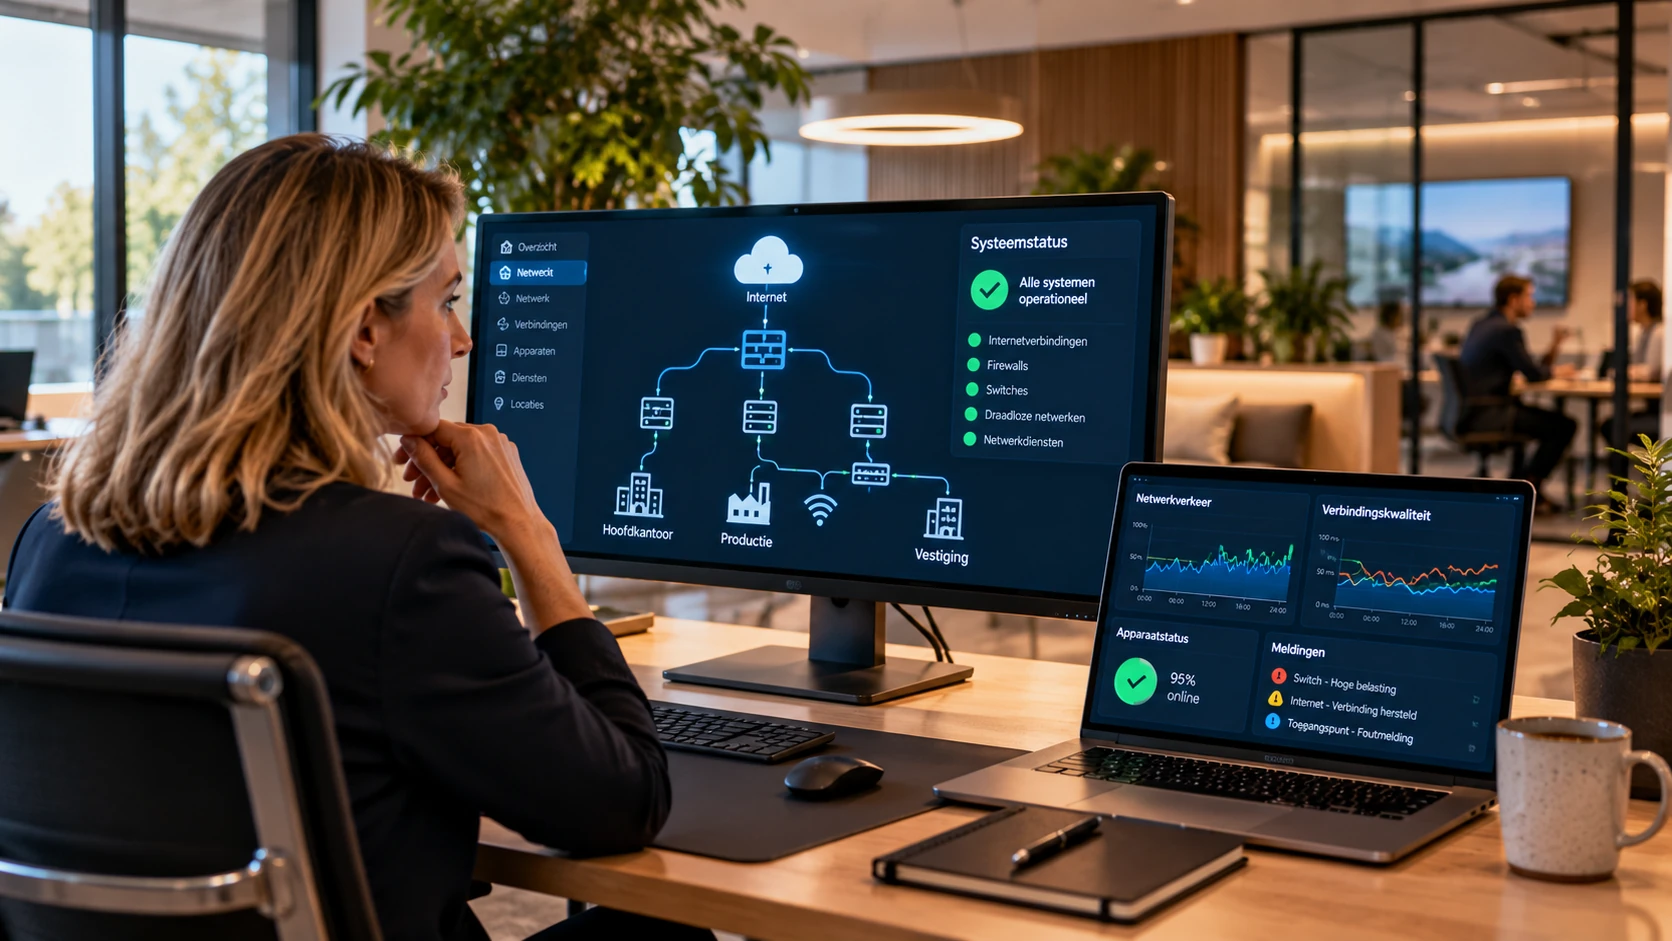
An employee opens a file on their workstation. A production machine exchanges data with a central server. An external supplier connects to carry out maintenance. Printers, cameras, wireless devices and building management systems may also be connected to the same business network.
All these devices and systems need network access, but not necessarily to the same parts of the IT environment. Yet business networks have often grown over the years in ways that allow systems to reach one another far more easily than their functions require.
As long as everything works properly, this usually goes unnoticed. But when a workstation is compromised, a supplier gains unwanted access or a device proves inadequately secured, that connectivity can considerably increase the consequences.
Network segmentation is therefore about more than dividing up a network. It is about controlling which systems are allowed to communicate with one another, and under what conditions.
A network grows, but its access boundaries do not automatically grow with it
Business networks are rarely designed in one go and then used unchanged for years. Organisations introduce new applications, expand production sites, connect locations and give suppliers access to the systems they need to maintain.
Connections are added with every expansion. A new server needs to be accessible from certain workstations. A production machine needs to exchange data with an ERP system. A supplier needs access to an operating system or industrial installation. The focus is often on whether the connection works, with less attention to which other systems become accessible as a result.
Over time, this can create an environment in which different types of equipment share the same network, or in which hardly any restrictions apply between networks. However, an administrative workstation, a wireless guest connection and a production environment have very different risk profiles.
This does not mean that these parts must be completely isolated from one another. It does mean that communication between them should be a deliberate choice, rather than an automatic consequence of the network design.
What is network segmentation?
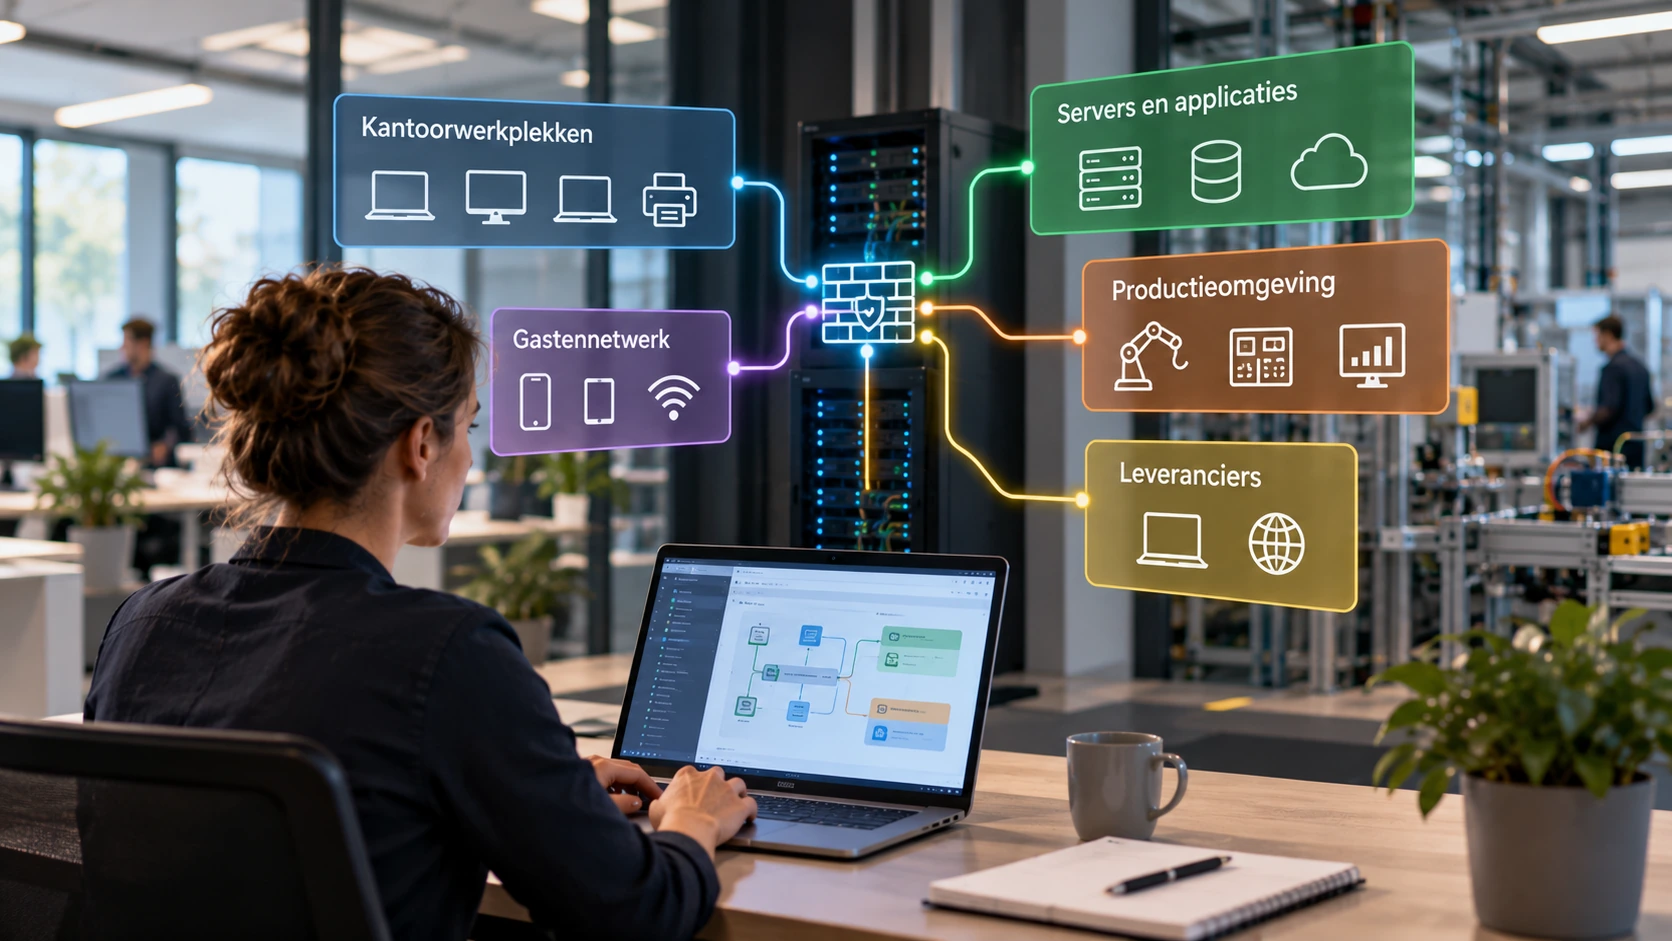
Network segmentation means dividing a network into separate parts and controlling communication between those parts. Which systems are allowed to communicate with one another is determined by their functions, the data they need to exchange and the associated risks.
An organisation might, for example, distinguish between office workstations, servers, production equipment, guest networks and building management systems. Further separation may then be needed within those parts, depending on the sensitivity of the systems and the consequences of a disruption.
Technically, network segmentation is often implemented using VLANs, routers, firewalls and access rules. A VLAN can logically place devices in a separate network, but does not in itself provide a complete security measure. If traffic between VLANs is allowed through without restrictions, there is a technical division, but hardly any effective access control.
What matters most is therefore not how many segments a network has, but which communication between those segments is actually permitted.
The difference between an open and a segmented network
Network with little segmentation
In an environment with little segmentation, systems can often connect to many other devices and services, even when this is unnecessary for their day-to-day work. An attacker who gains access to one part of the network may therefore be able to approach, investigate or attack other systems.
- Systems can often reach one another without a clear functional need.
- A compromised device may have access to other parts of the network.
- It is more difficult to apply appropriate security rules to each group of systems.
Segmented network
In a well-segmented network, that freedom of movement is more limited. Workstations can, for example, access the business applications they need without having direct access to the management interfaces of network equipment or production systems. A guest network provides internet access, but no access to internal business resources.
- Communication between parts of the network is restricted to necessary connections.
- An incident can be contained more effectively because not all systems are directly accessible.
- Access rules can be tailored to function, sensitivity and business importance.
Segmentation does not prevent a system from being attacked or compromised. It can, however, limit the opportunities to reach other parts of the organisation from that system. This makes network segmentation an important measure for reducing the impact of security incidents.
Why network segmentation is particularly important in production environments
Manufacturing businesses often bring together several generations of technology. Modern office workstations and cloud applications operate alongside machines and industrial control systems that remain in use for many years.
Some of these systems use outdated operating systems or communication protocols. Software updates are not always straightforward, for example because the manufacturer prescribes a specific configuration or because an update could affect a production process.
It is particularly important in such environments to carefully restrict which systems can be accessed. A production machine generally does not need to be directly accessible from every office workstation. An external maintenance provider may need access to one specific installation, but not to the entire production environment.
The actual communication requirements must be taken into account. Production systems may depend on central databases, planning software, file transfers or other resources. Blocking network connections without sufficient investigation can disrupt production.
Network segmentation therefore requires cooperation between IT management, production, application owners and suppliers. Business processes, as well as technical capabilities, determine how the separation should be implemented.
Four considerations for effective segmentation
1. Understanding systems and dependencies
Map the devices, applications and services in use and the communication they require. Without this understanding, necessary connections may be blocked or unwanted connections may remain open.2. Separation based on function and risk
Do not group systems solely by physical location or technical characteristics. Also consider their role in business operations, the sensitivity of the data and the consequences of a system being compromised.3. Controlling communication between segments
Explicitly determine which connections between segments are permitted. Restrict access to management interfaces, servers and other critical resources to the systems and users that actually need it.4. Reviewing and maintaining access rules
Networks change constantly. New applications, suppliers and equipment may require new connections. Periodically check whether existing access rules still suit the current environment.
Effective segmentation is not a one-off configuration, but part of ongoing network management.
Segmentation only works when access rules are enforced
A network may be carefully divided on paper while providing far less protection in practice. This happens, for example, when broad firewall rules are configured between segments to prevent communication problems.
A rule allowing all connections from an office segment to a server segment may make the network easier to organise, but does little to restrict access rights. The same applies when management interfaces remain accessible from general-purpose workstations, or when external suppliers gain VPN access to a much larger part of the network than necessary.
Access rules must therefore match actual communication requirements as closely as possible. Wherever possible, only necessary traffic is permitted, for example between specific systems and for particular applications or services.
Management connections also deserve separate attention. Access to switches, firewalls, hypervisors and other central infrastructure often provides extensive capabilities to affect the IT environment. It is therefore sensible to separate this access from ordinary user traffic and apply additional security measures.
Segmentation is also closely linked to identity and access management. A network connection being technically permitted does not mean that every user or supplier should be allowed to access the application behind it. These two forms of access control complement one another.
What does network segmentation mean for continuity?
The value of network segmentation is often considered primarily from a cybersecurity perspective. However, a clear network structure can also be important for the availability and manageability of the IT environment.
When an incident remains confined to a particular part of the network, other systems may be able to keep functioning. This can help limit the consequences for business operations and allow more targeted recovery measures.
At the same time, segmentation introduces dependencies on network equipment and security rules. An incorrect firewall rule can make a business application inaccessible. A failure in a central network component can affect several segments. The availability, capacity and management of network resources must therefore meet the organisation's requirements.
Segmentation also plays a role in recovery after an incident. When systems are rebuilt, it must be clear which network connections they need and under what conditions they may communicate with other parts of the environment again. A segmented design can help keep recovery under control, provided that the configuration is properly documented and the necessary dependencies are known.
How do you approach network segmentation in an existing environment?
For many organisations, redesigning the entire network in one go is not realistic. A change requires careful preparation, particularly when business applications, production machines and supplier connections depend on one another.
A sensible approach therefore starts with understanding the environment. Which parts of the network exist, which systems are connected to them and which connections are actually used? The next step is to determine where the greatest risks lie and which separation would provide the most value.
Sometimes it makes sense to isolate guest networks and building management equipment first. In other environments, protecting servers, management resources or industrial systems takes priority. The right order depends on business processes and existing security measures.
Changes must be implemented and tested in a controlled manner. It is important to check both that unwanted communication is blocked and that necessary applications and processes continue to function. This allows network segmentation to be improved step by step without unnecessarily disrupting business operations.
Network segmentation is a management choice, not a one-off project
A sound network structure provides an important foundation for security, but only retains its value when it is incorporated into day-to-day IT management.
New equipment must be placed in the right network segment. New applications require an assessment of the connections they need. Supplier access must be tailored to the systems for which that access is necessary. And when business processes change, the associated network rules must be reassessed.
Malenco therefore approaches network segmentation as part of security-focused IT management, rather than as an isolated technical intervention. The design must suit business operations, reduce risks and remain manageable in practice.
The aim is not to separate as many networks as possible, but to enable precisely the connections the organisation needs — and deliberately restrict the others.